SOC Audits
SOC Audits that Deliver Credibility and Compliance
SC&H delivers SOC audits with the hands-on readiness support and long-term partnership that other firms skip. We’ll help you gain compliance that’s built to trust, instead of simply checking a box.
- Work with a team that responds quickly, within 24 hours
- Keep the same senior team year over year, no re-explaining your business
- Get SOC 1, SOC 2, and SOC 3 examinations, all under one roof
Determine the right SOC report for your organization
Not sure which SOC report fits your needs? Let’s figure it out.
SOC 1
SOC 2
SOC 3
What it covers
Controls relevant to your clients’ financial reporting
Controls relevant to AICPA’s Trust Services Criteria: Security, and (as applicable) Availability, Confidentiality, Processing Integrity, Privacy
High-level summary of SOC 2, for public use
Best fit if
Your services affect a client’s financial statements or SOX 404 compliance
Your clients need confidence in how you store and protect their data
You want a public-facing report you can share for marketing/credibility
Who can see it
Restricted- Your management and your client’s auditors
Restricted- Your management, clients, regulators, and other informed parties
Unrestricted- Anyone
Type 1 and 2?
Yes
Yes
No
The right level of support for your SOC audit needs
From readiness support to ongoing advisory, our team delivers support designed to meet your organization where it is.
Full-service
We manage your entire SOC journey, from initial readiness through the final report, so you have one team the whole way through.
Get startedAudit only
If you’ve already prepared internally or with another advisor, we step in to perform the formal examination and get your report issued.
Get startedAdvisory
Beyond the audit itself, we stay on as your ongoing resource for control reviews, next year’s prep, and adding frameworks like ISO or SSPA.
get startedOur SOC audit process
Here’s how our team conducts performance audit engagements, which are further tailored based on multiple factors including risks, objectives, scope, and the organization’s environment:
Unlock additional frameworks faster
We standardize our audit process across multiple frameworks to save you time and money. That means when you complete your SOC 2 audit with SC&H, you’re already well on your way to ISO and Microsoft SSPA compliance. Getting these certifications is faster and easier than ever.
ISO certification↗ Microsoft SSPA↗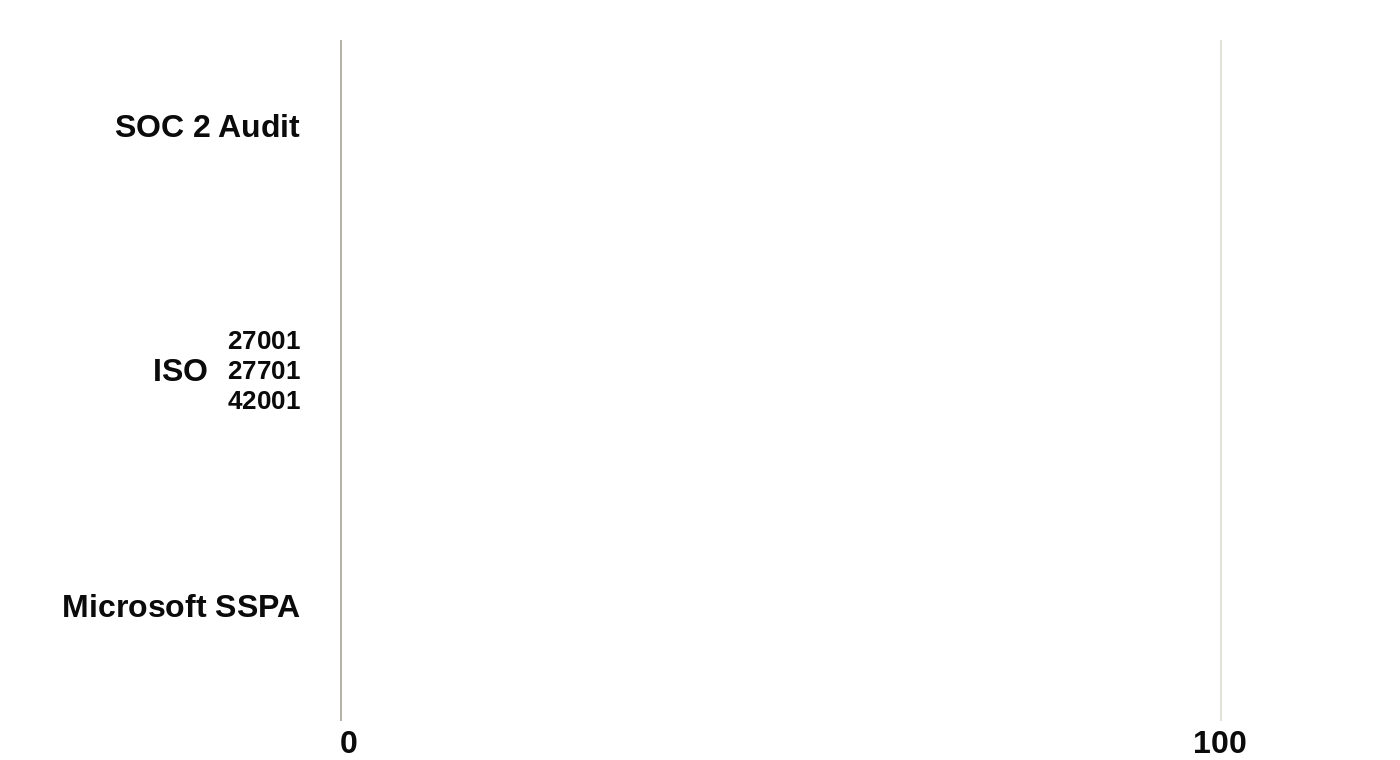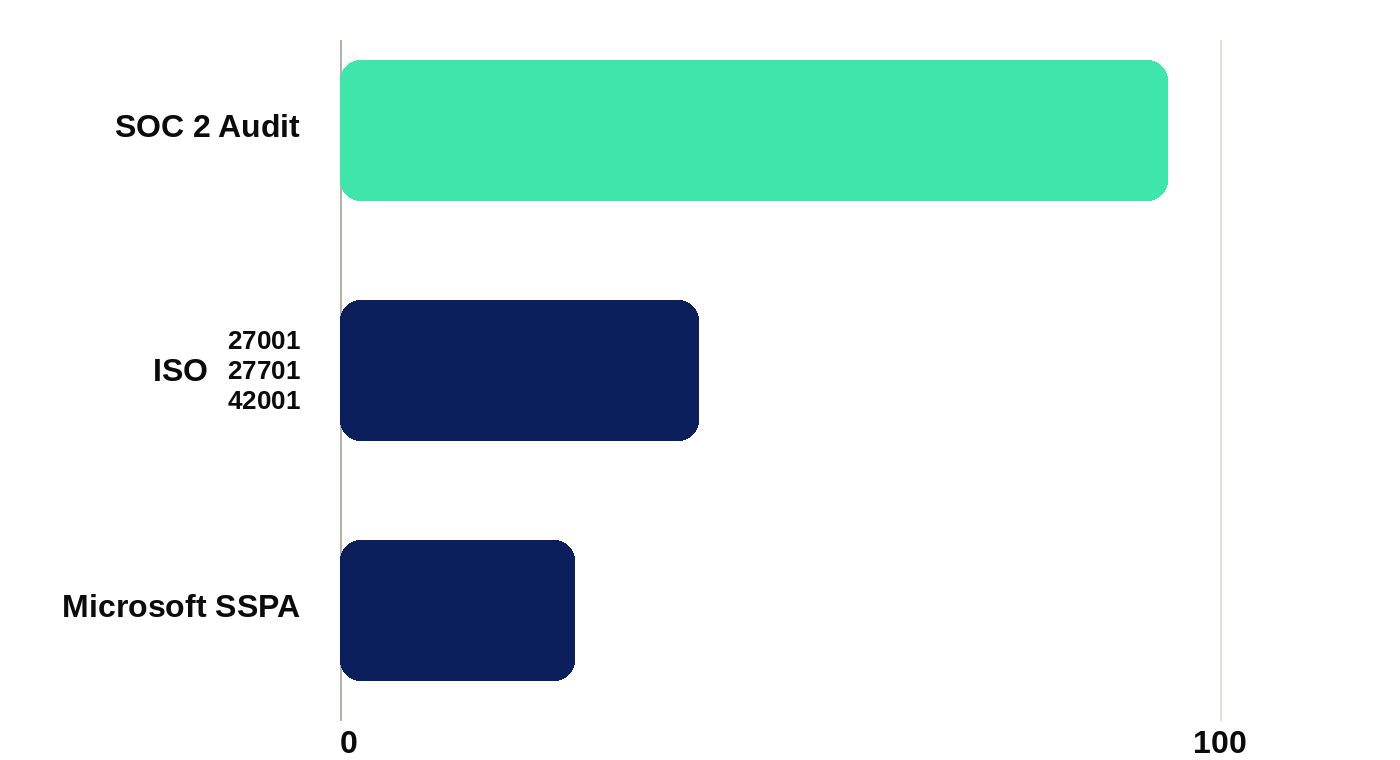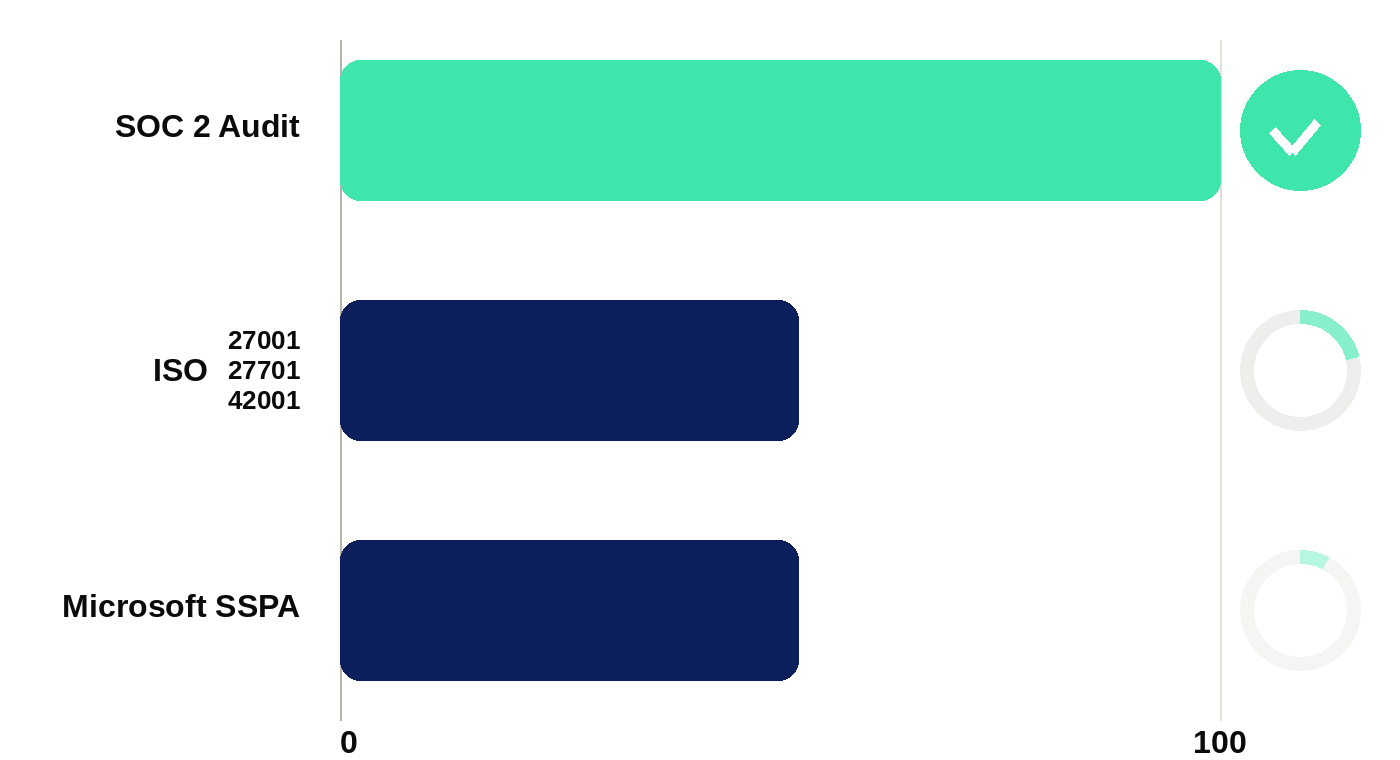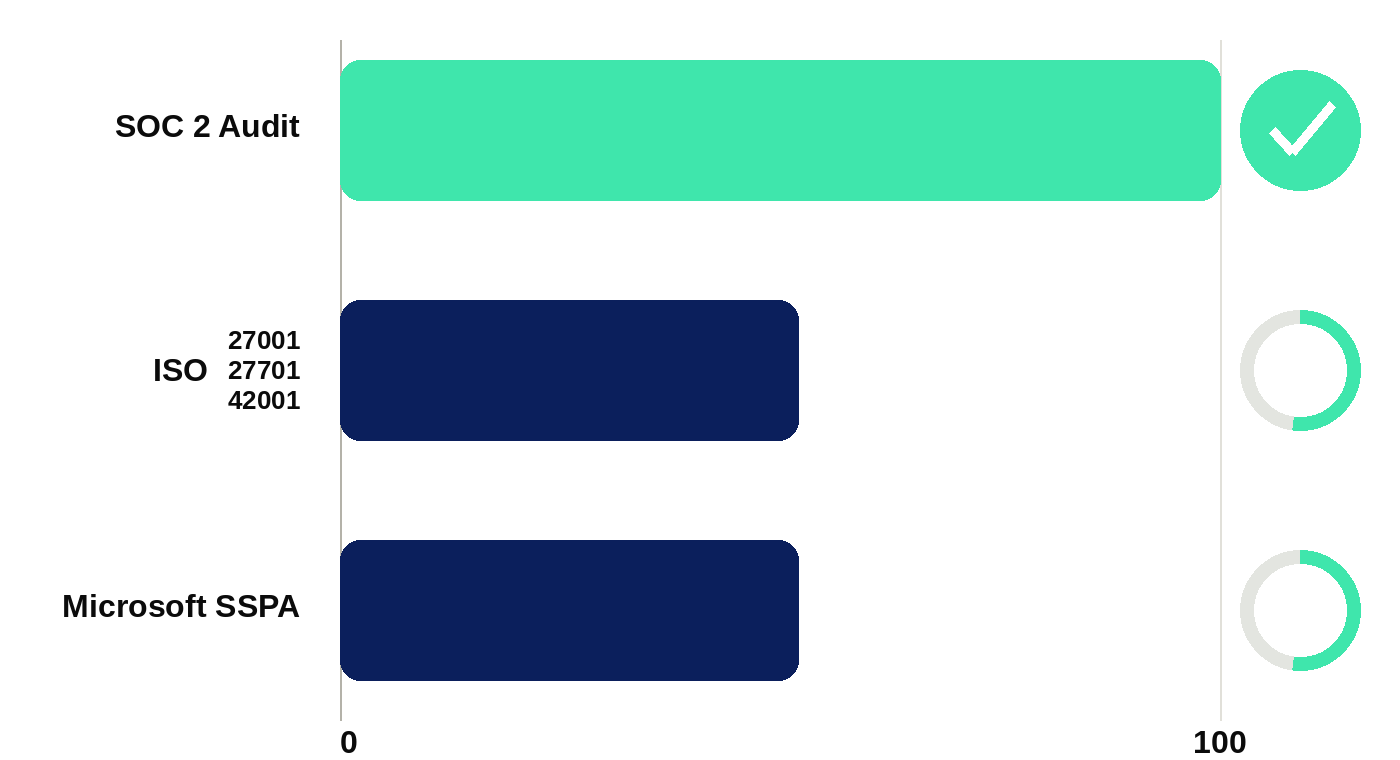
Technology keeping your audit on track
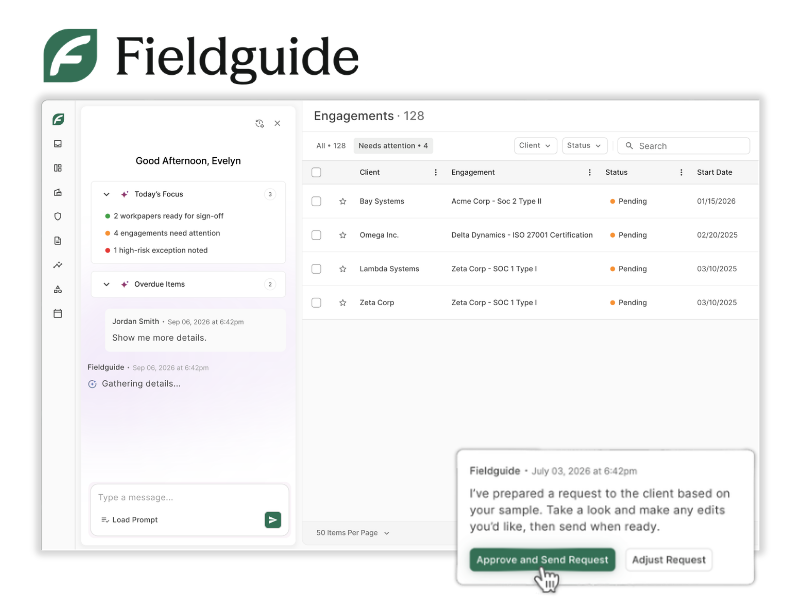
Automate up to 25% of certification management with our AI-powered audit platform, Fieldguide. This secure platform offers a user-friendly interface and built-in, intuitive dashboards offering:
- Easy document uploads
- Real-time chat to communicate with your auditor
- Built-in timelines
- Reduce emails throughout the audit process
“SC&H was instrumental in helping EPS Learning achieve our SOC 2 Type II attestation. We could not have achieved this milestone as quickly or smoothly without their partnership, professionalism, and ongoing support.”
Monte Kalisch
VP Technology, EPS Learning
Why you’ll love working with SC&H

A team that sticks around
Our leadership has stayed with us for an average of 12 years, so there’s no relearning your business every audit cycle.

Long-term partner
We’re not a firm you call once a year. We stay engaged with wrap-up calls, recommendations, and a team that will always pick up the phone.

Governance, risk & compliance platform
We bring hands-on experience auditing through providers like Vanta, Drata, and ControlMap, integrating with the tools you already use.

Customized controls
We review and update your controls every year, instead of auditing against a checklist that no longer reflects how your business runs.
SOC audit FAQs
Any organization that outsources services will typically request a SOC report from a current or prospective service provider to ensure the provider has controls in place to protect their data and/or delivery of services.
Common scenarios that trigger a request for a SOC report:
- Outsourcing payroll, credit-card processing, recordkeeping, etc.
- Using software as a service (SaaS)
- Storing sensitive data with a cloud service provider
- When infrastructure / data are hosted or managed by an external third-party system
It’s not required, but we strongly recommend it, especially for your first audit. A readiness assessment lets us identify and close any gaps in your controls before the formal examination begins, so there are no surprises once fieldwork starts.
Type 1 Report: describes a service organization’s suitability of the design and implementation of controls at a specific point in time
Type 2 Report: goes further, ensuring that those controls are consistently operating effectively over a defined period of time –thus yielding improved operational performance.
We work with organizations across a wide range of industries including:
- SaaS
- Healthcare
- Managed service providers (MSP)
- Financial services
- Legal
- Mineral management/Land management
- And more
If your industry isn’t listed here, reach out. SOC audits apply to nearly any organization that handles client data or outsourced services.
It depends on your audit period and where you’re starting from. Fieldwork itself takes as little as 3-4 weeks once it begins, with timing tailored to your organization, but the audit period you’re being examined over can range from as short as 3 months to a full 12 months.
Yes. SC&H performs SOC, ISO 27001/27701/42001, and Microsoft SSPA audits in-house, and because these frameworks share significant overlap in required controls, completely one often puts you well on your way to the others.
Meet Your SOC Audit Experts

You deserve more than a checkbox audit
A SOC examination shouldn’t feel like a checkbox you’re rushing to complete. SC&H prepares you before the audit, stays with you after the report is issued, and helps you turn one certification into the next.
book a consultation